Hardware, interfaces, and modules
Track physical devices, their network endpoints, and installed components. Review identity conflicts and retain replacement history.
 OTserver — Open-Source Industrial Asset ManagementOpen-Source Industrial Asset ManagementOTserver — Open-Source Industrial Asset ManagementOpen-Source Industrial Asset Management
Open source asset management and discovery
Discover industrial devices with OTserver Otter and keep their hardware identity, software versions, network connections, and source evidence in one inventory hosted on your infrastructure. Schedule scans by site and review the vulnerability advisories that match your equipment.
One trustworthy inventory
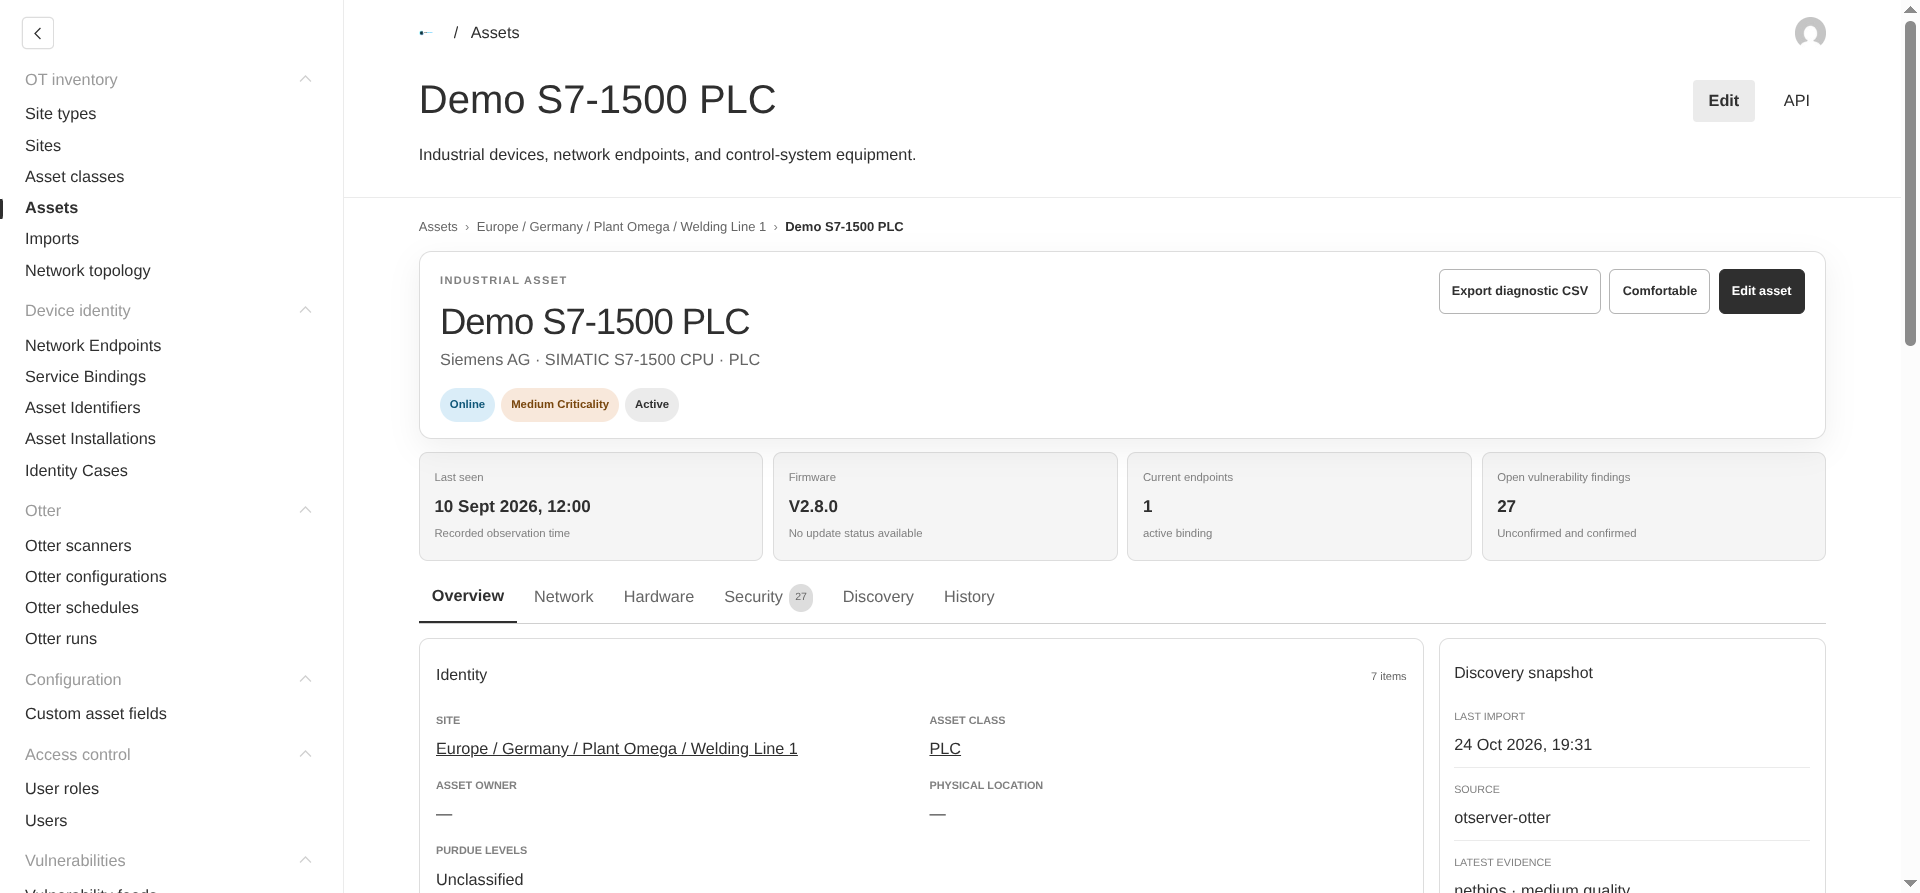
Import Otter discovery results into the right site. OTserver separates physical hardware from network endpoints, links qualified hardware identities across interfaces, and preserves human edits when new evidence arrives.
Track physical devices, their network endpoints, and installed components. Review identity conflicts and retain replacement history.
Match recorded versions against NVD and CSAF advisories. Confirm or dismiss potential matches, then track confirmed findings through resolution.
Grant read or write access by site and retain an immutable audit log that redacts secrets.
Vulnerability management
OTserver compares recorded vendor, product, operating system, and version data with locally stored NVD and CSAF advisories. CISA KEV highlights known exploitation, and the ICS Advisory Project adds industrial advisory context.
Filter findings by severity, inspect the evidence for affected versions, and record your review. Confirmed findings stay open until you resolve them, even if a later import changes the matching evidence.
Matching uses inventory evidence without sending vulnerability probes to devices. For disconnected installations, transfer publisher feed files and import them into the local catalog.
Read the vulnerability management guide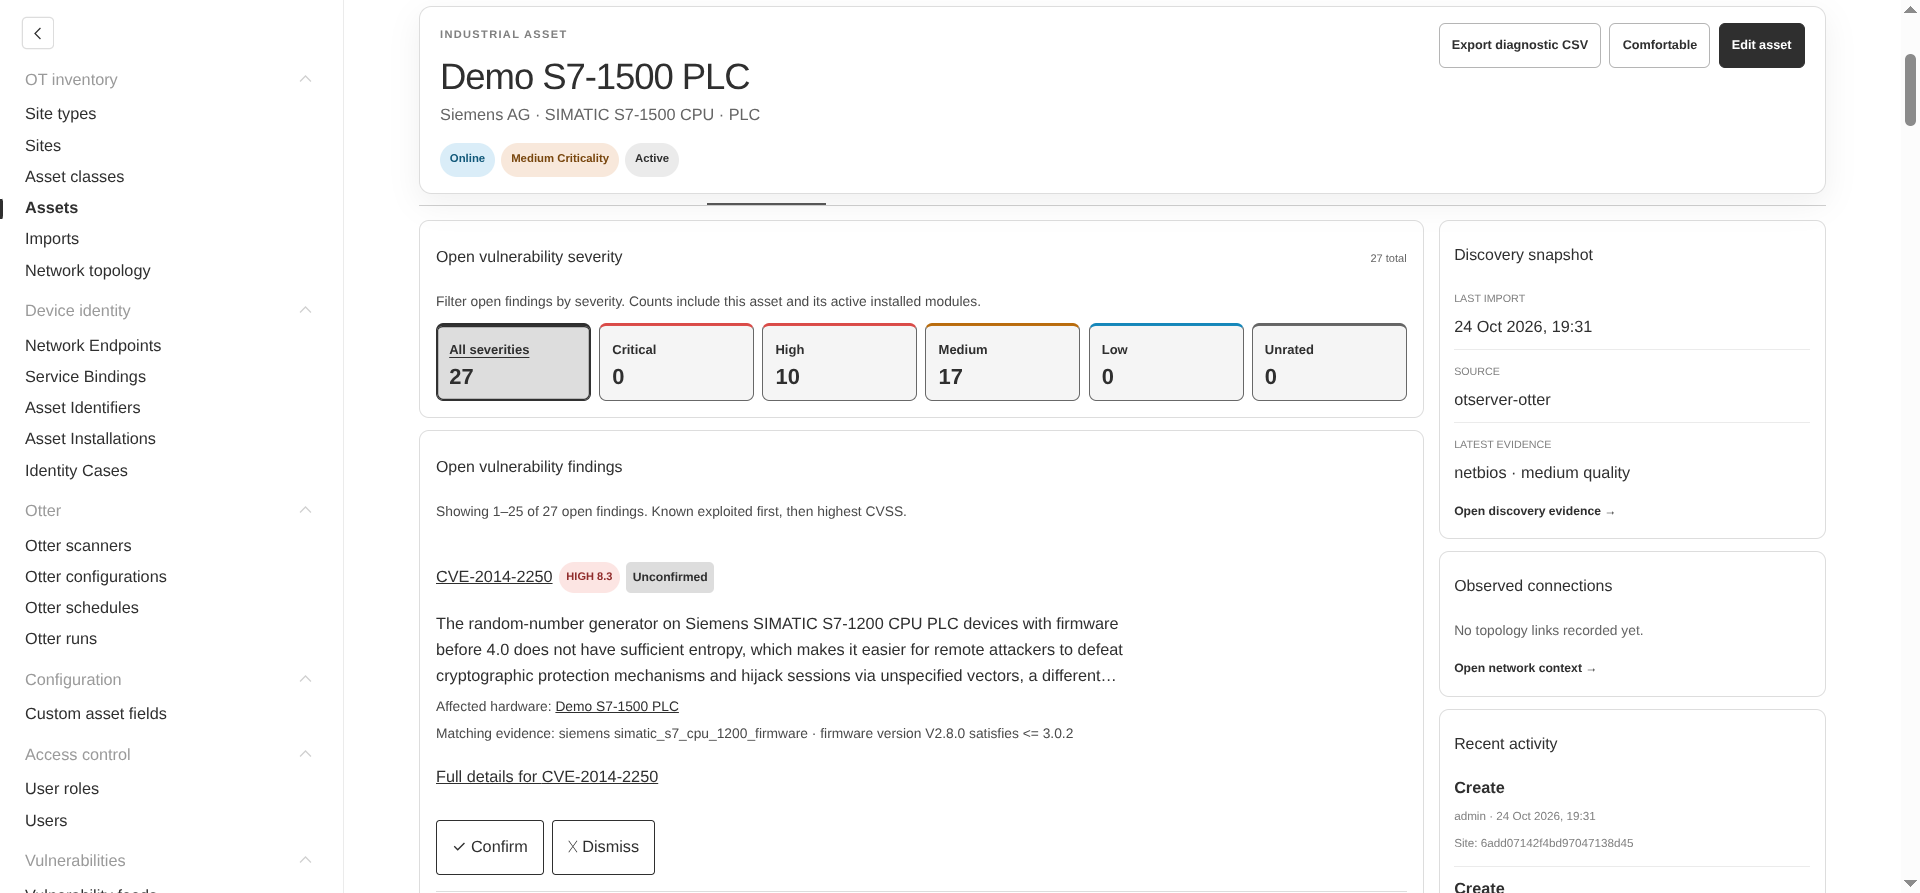
Inside OTserver
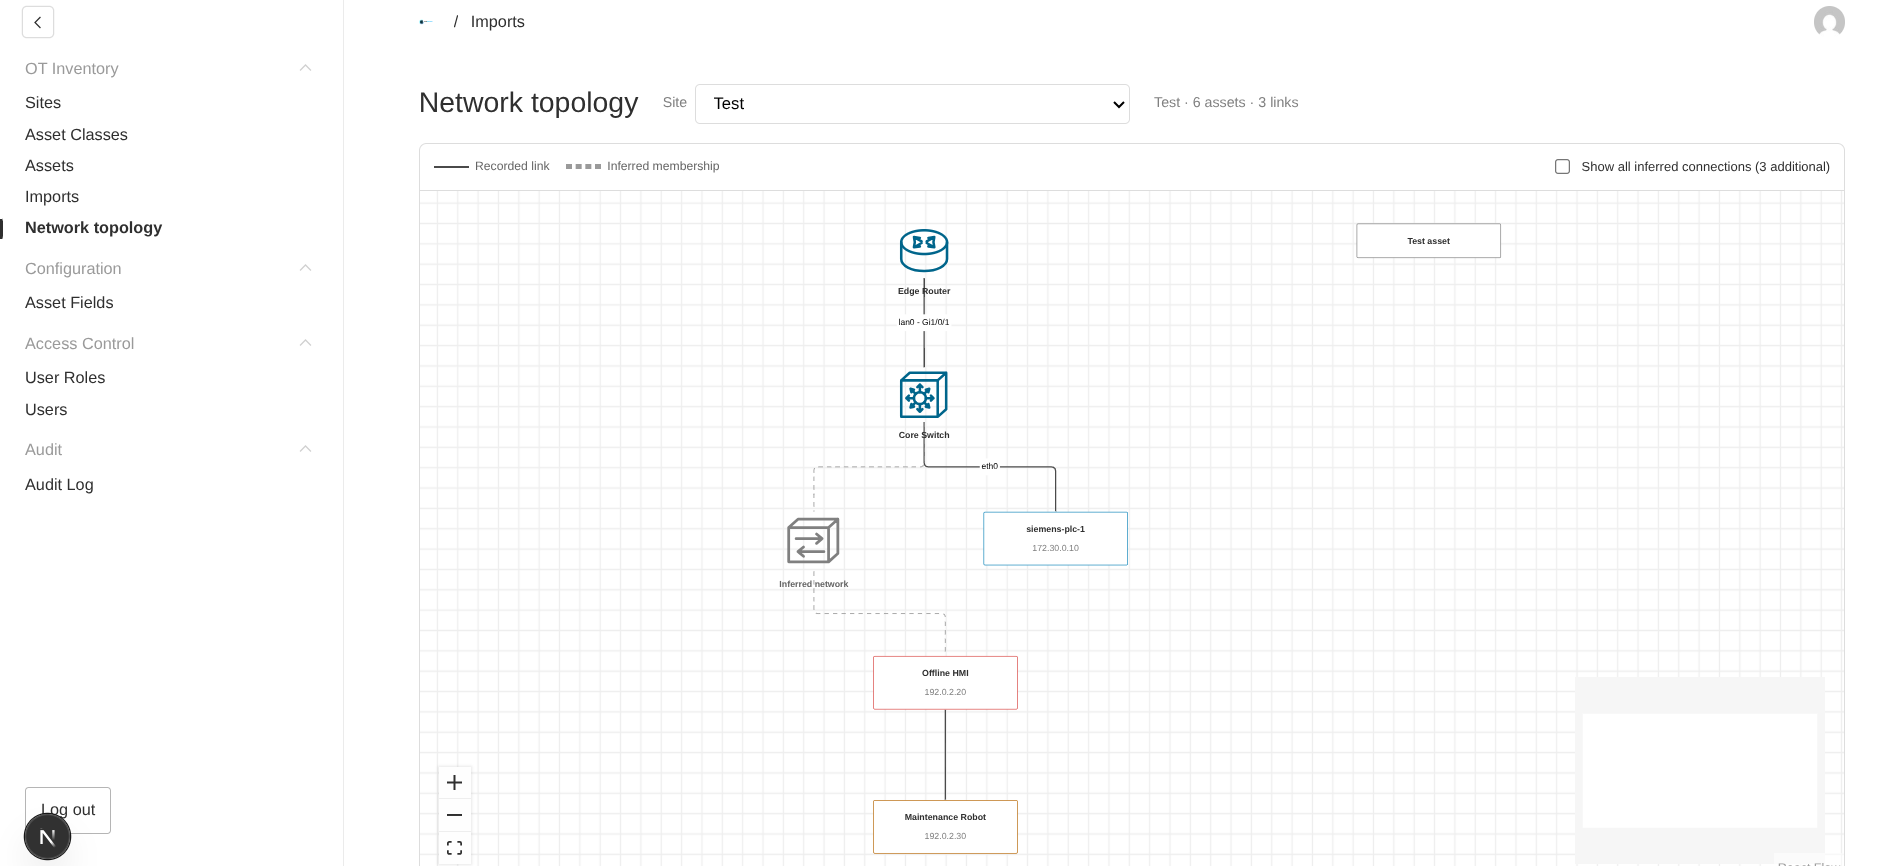
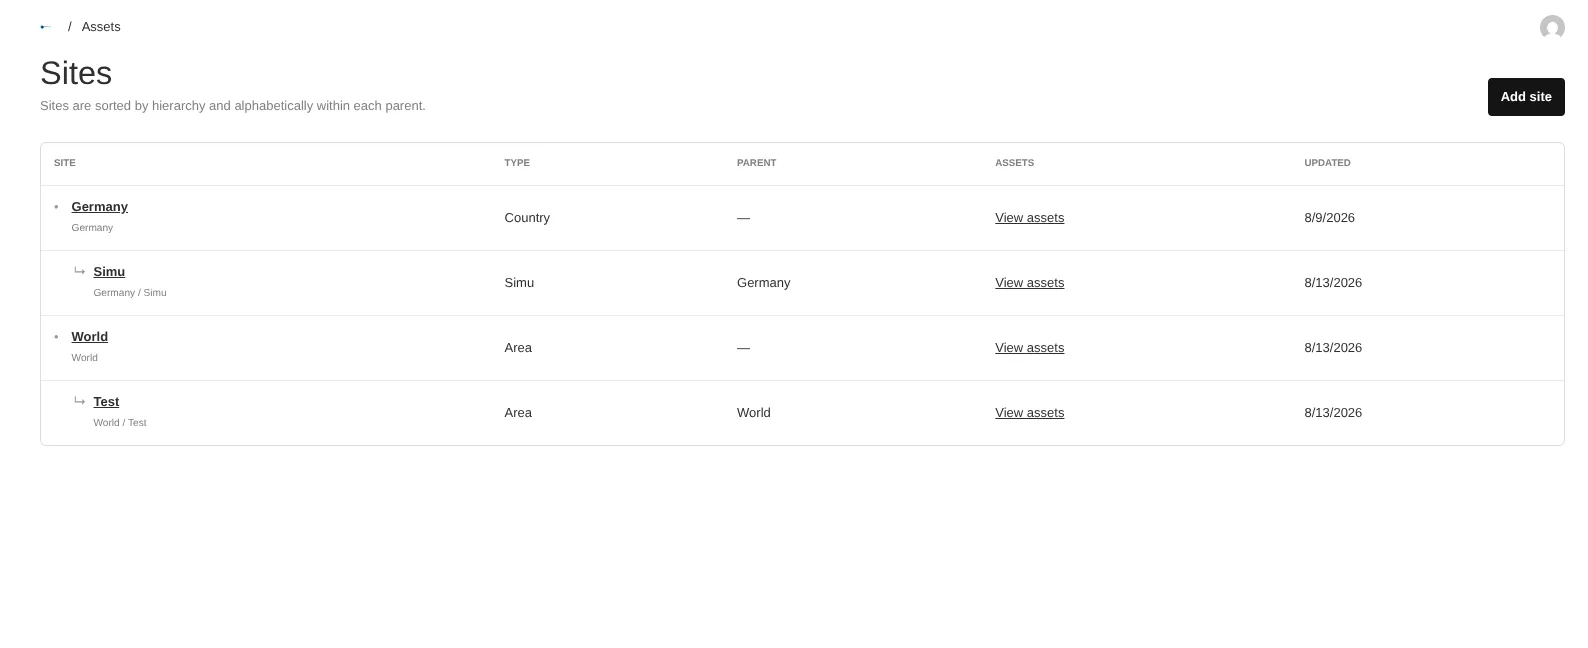
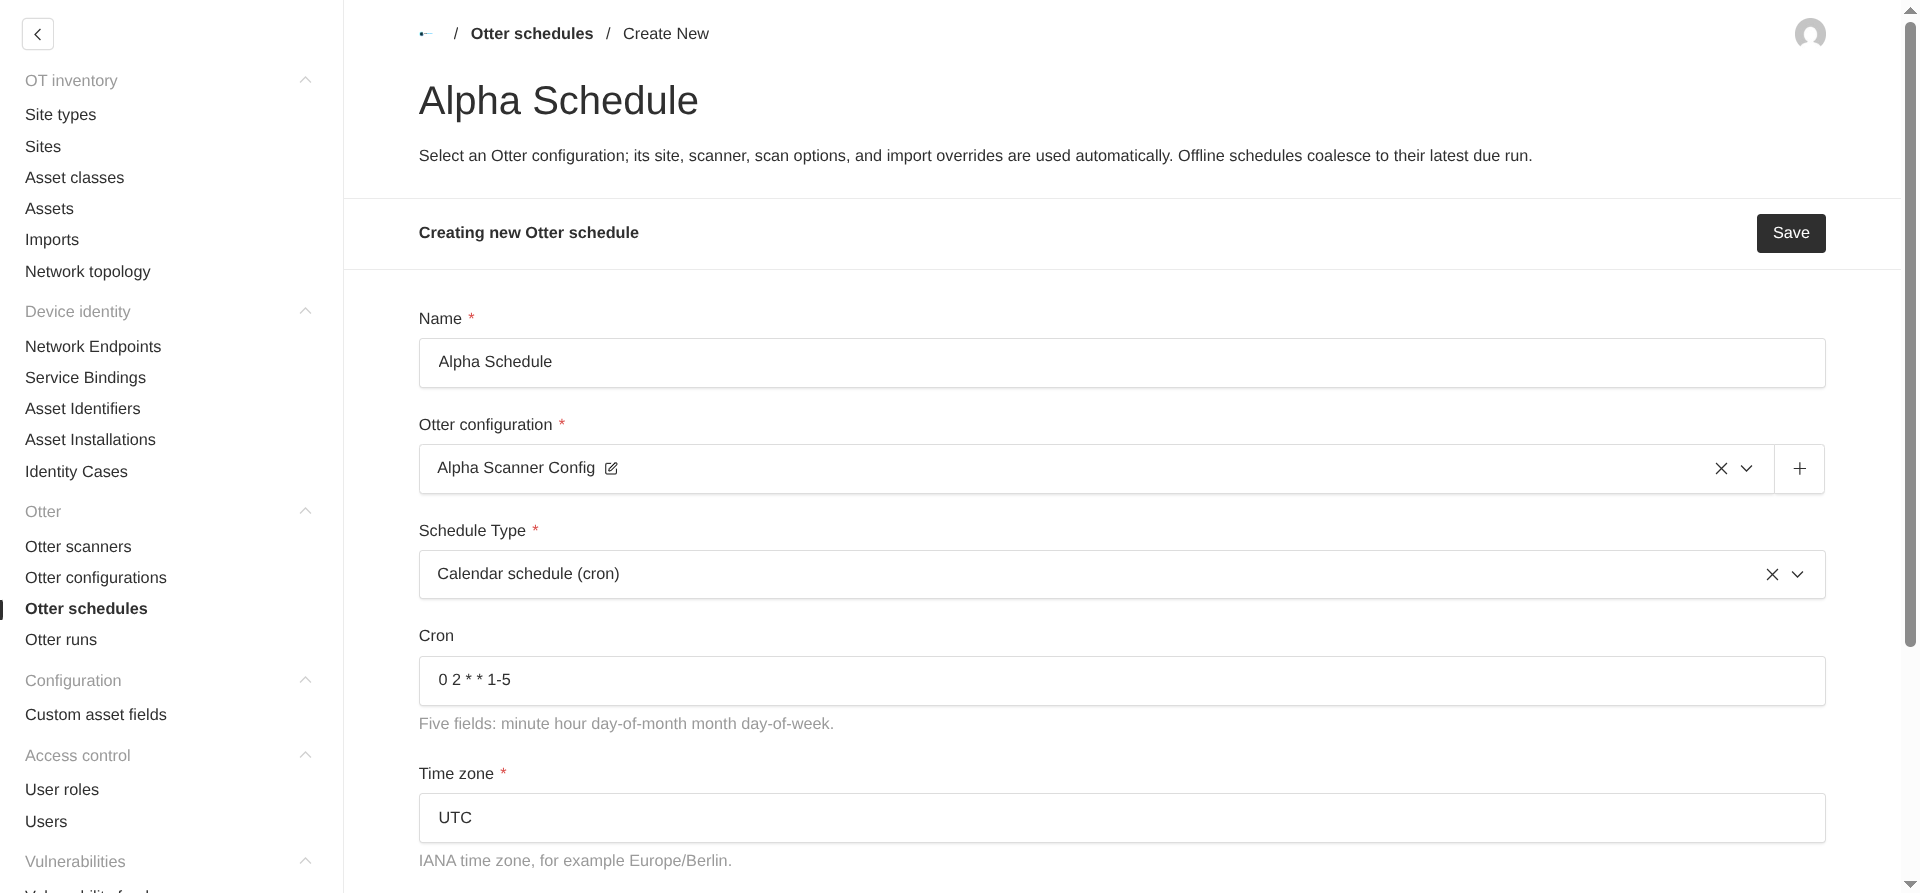
These product screenshots use demonstration data to show site structure, scan scheduling, imports, and recorded network connections.

OTserver Otter: read only discovery
Otter collects industrial identity and topology through ARP, PROFINET DCP and PNIO, S7, EtherNet/IP, BACnet, Omron FINS, Beckhoff ADS, Niagara Fox, DNP3, IEC 61850, OPC UA, SNMP, and LLDP. NetBIOS and SMB/RPC add computer names and reported OS evidence; HTTP/HTTPS records web service responses.
Use the Windows or Linux GUI for local exports, the CLI for direct uploads, or install a managed controller to run scheduled scans in the background. Discovery requires explicit authorization.
Manage Otter scanners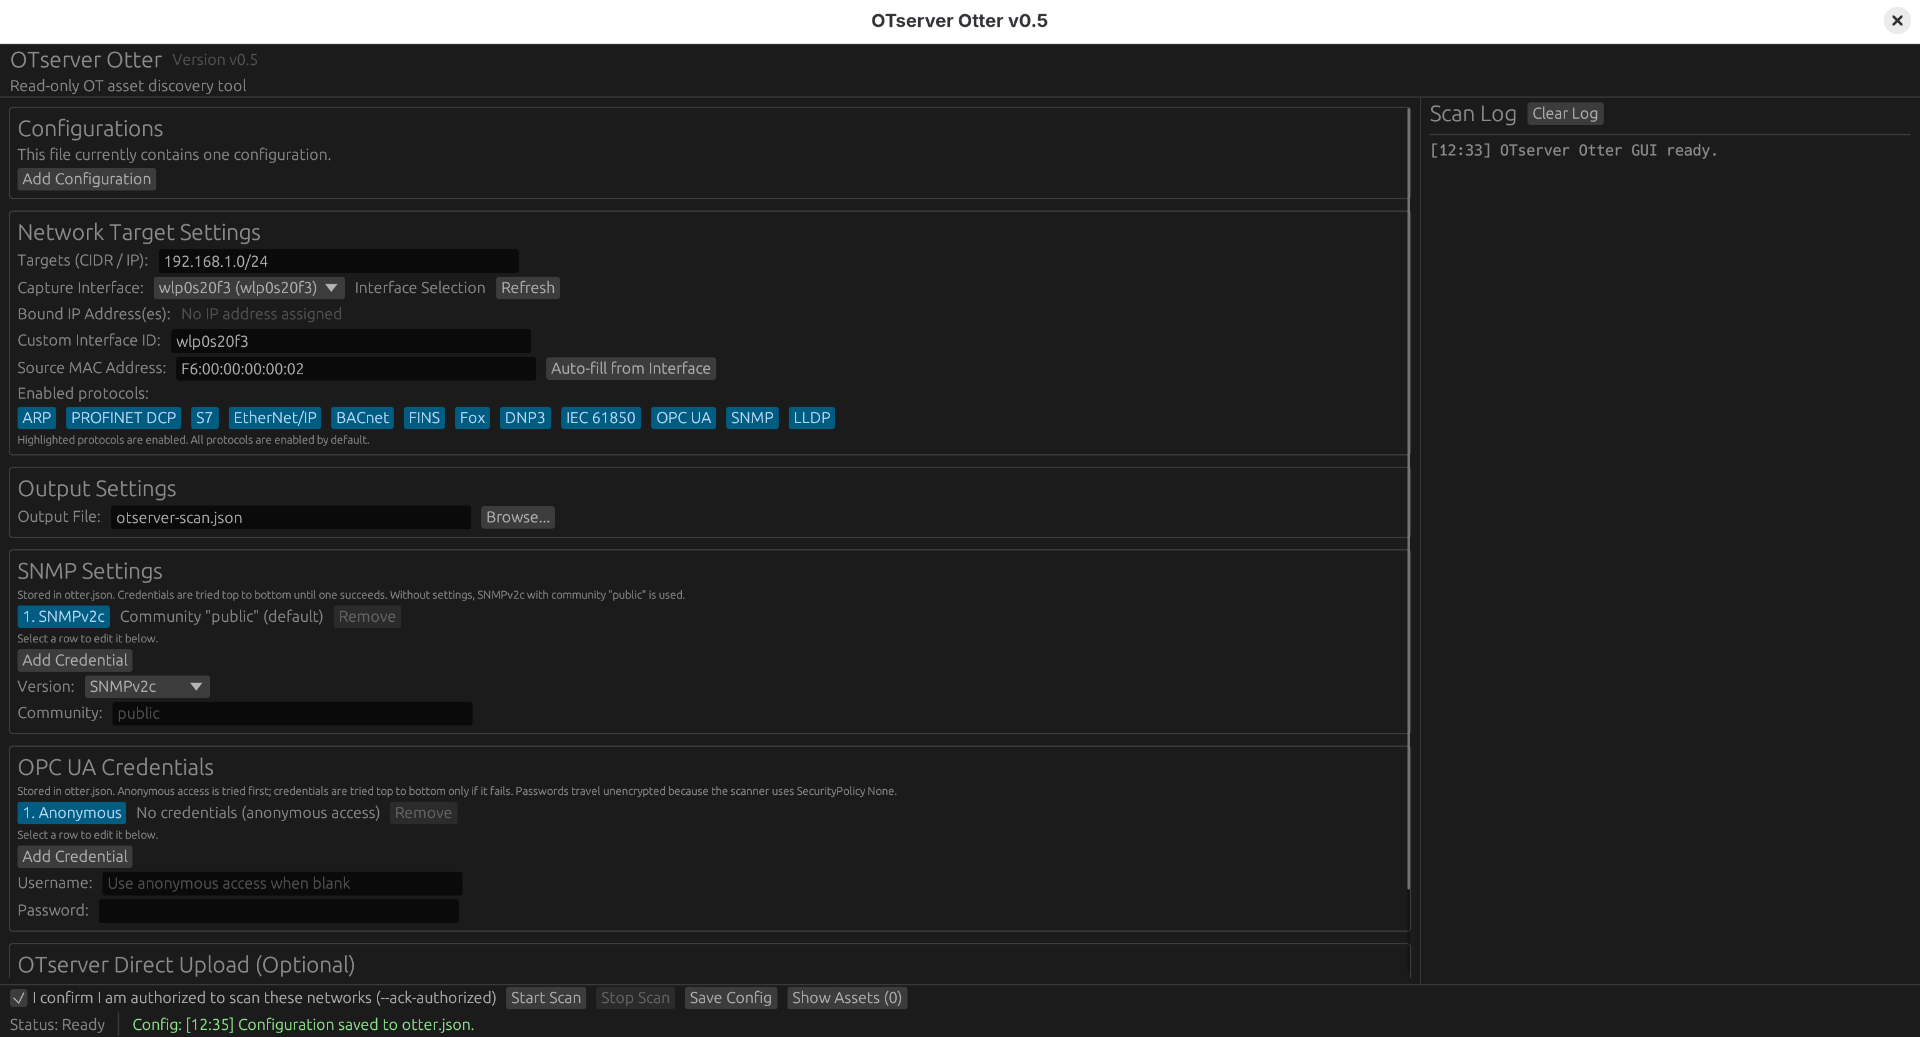
Run it yourself or let us manage it
Deploy OTserver on your own infrastructure. Both repositories are developed in the open: the OTserver application and the OTserver Otter scanner. For the enterprise version or managed hosting, talk to us.